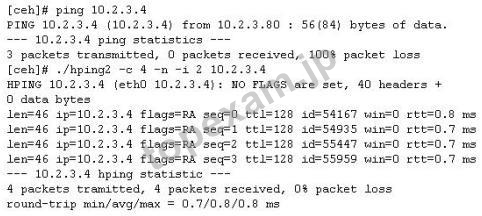
質問 1:You ping a target IP to check if the host is up. You do not get a response. You suspect ICMP is blocked at the firewall. Next you use hping2 tool to ping the target host and you get a response. Why does the host respond to hping2 and not ping packet?
 A.
You must use ping 10.2.3.4 switch
B. Hping2 uses TCP instead of ICMP by default
C. Hping2 uses stealth TCP packets to connect
D. Ping packets cannot bypass firewalls
正解:B
質問 2:A security analyst in an insurance company is assigned to test a new web application that will be used by clients to help them choose and apply for an insurance plan. The analyst discovers that the application is developed in ASP scripting language and it uses MSSQL as a database backend. The analyst locates the application's search form and introduces the following code in the search input fielD.
IMG SRC=vbscript:msgbox("Vulnerable");> originalAttribute="SRC" originalPath="vbscript:msgbox("Vulnerable");>" When the analyst submits the form, the browser returns a pop-up window that says "Vulnerable".
Which web applications vulnerability did the analyst discover?
A. Cross-site request forgery
B. SQL injection
C. Command injection
D. Cross-site scripting
正解:D
質問 3:When discussing passwords, what is considered a brute force attack?
A. You wait until the password expires
B. You threaten to use the rubber hose on someone unless they reveal their password
C. You create hashes of a large number of words and compare it with the encrypted passwords
D. You load a dictionary of words into your cracking program
E. You attempt every single possibility until you exhaust all possible combinations or discover the password
正解:E
解説: (Topexam メンバーにのみ表示されます)
質問 4:The SYN flood attack sends TCP connections requests faster than a machine can process them.
Attacker creates a random source address for each packet
SYN flag set in each packet is a request to open a new connection to the server from the spoofed IP address Victim responds to spoofed IP address, then waits for confirmation that never arrives (timeout wait is about 3 minutes) Victim's connection table fills up waiting for replies and ignores new connections Legitimate users are ignored and will not be able to access the server How do you protect your network against SYN Flood attacks?
A. SYN cookies. Instead of allocating a record, send a SYN-ACK with a carefully constructed sequence number generated as a hash of the clients IP address, port number, and other information. When the client responds with a normal ACK, that special sequence number will be included, which the server then verifies. Thus, the server first allocates memory on the third packet of the handshake, not the first.
B. Micro Blocks. Instead of allocating a complete connection, simply allocate a micro record of 16-bytes for the incoming SYN object
C. Stack Tweaking. TCP stacks can be tweaked in order to reduce the effect of SYN floods. Reduce the timeout before a stack frees up the memory allocated for a connection
D. RST cookies - The server sends a wrong SYN/ACK back to the client. The client should then generate a RST packet telling the server that something is wrong. At this point, the server knows the client is valid and will now accept incoming connections from that client normally
E. Check the incoming packet's IP address with the SPAM database on the Internet and enable the filter using ACLs at the Firewall
正解:A,B,C,D
質問 5:How can telnet be used to fingerprint a web server?
A. telnet webserverAddress 80
PUT / HTTP/1.0
B. telnet webserverAddress 80
HEAD / HTTP/1.0
C. telnet webserverAddress 80
HEAD / HTTP/2.0
D. telnet webserverAddress 80
PUT / HTTP/2.0
正解:B
質問 6:A user on your Windows 2000 network has discovered that he can use L0phtcrack to sniff the SMB exchanges which carry user logons. The user is plugged into a hub with 23 other systems. However, he is unable to capture any logons though he knows that other users are logging in.
What do you think is the most likely reason behind this?
A. Kerberos is preventing it.
B. There is a NIDS present on that segment.
C. L0phtcrack only sniffs logons to web servers.
D. Windows logons cannot be sniffed.
正解:A
解説: (Topexam メンバーにのみ表示されます)
TopExamは君にEC0-350の問題集を提供して、あなたの試験への復習にヘルプを提供して、君に難しい専門知識を楽に勉強させます。TopExamは君の試験への合格を期待しています。
安全的な支払方式を利用しています
Credit Cardは今まで全世界の一番安全の支払方式です。少数の手続きの費用かかる必要がありますとはいえ、保障があります。お客様の利益を保障するために、弊社のEC0-350問題集は全部Credit Cardで支払われることができます。
領収書について:社名入りの領収書が必要な場合、メールで社名に記入していただき送信してください。弊社はPDF版の領収書を提供いたします。
弊社のEC-COUNCIL EC0-350を利用すれば試験に合格できます
弊社のEC-COUNCIL EC0-350は専門家たちが長年の経験を通して最新のシラバスに従って研究し出した勉強資料です。弊社はEC0-350問題集の質問と答えが間違いないのを保証いたします。

この問題集は過去のデータから分析して作成されて、カバー率が高くて、受験者としてのあなたを助けて時間とお金を節約して試験に合格する通過率を高めます。我々の問題集は的中率が高くて、100%の合格率を保証します。我々の高質量のEC-COUNCIL EC0-350を利用すれば、君は一回で試験に合格できます。
弊社は無料EC-COUNCIL EC0-350サンプルを提供します
お客様は問題集を購入する時、問題集の質量を心配するかもしれませんが、我々はこのことを解決するために、お客様に無料EC0-350サンプルを提供いたします。そうすると、お客様は購入する前にサンプルをダウンロードしてやってみることができます。君はこのEC0-350問題集は自分に適するかどうか判断して購入を決めることができます。
EC0-350試験ツール:あなたの訓練に便利をもたらすために、あなたは自分のペースによって複数のパソコンで設置できます。
一年間の無料更新サービスを提供します
君が弊社のEC-COUNCIL EC0-350をご購入になってから、我々の承諾する一年間の更新サービスが無料で得られています。弊社の専門家たちは毎日更新状態を検査していますから、この一年間、更新されたら、弊社は更新されたEC-COUNCIL EC0-350をお客様のメールアドレスにお送りいたします。だから、お客様はいつもタイムリーに更新の通知を受けることができます。我々は購入した一年間でお客様がずっと最新版のEC-COUNCIL EC0-350を持っていることを保証します。
弊社は失敗したら全額で返金することを承諾します
我々は弊社のEC0-350問題集に自信を持っていますから、試験に失敗したら返金する承諾をします。我々のEC-COUNCIL EC0-350を利用して君は試験に合格できると信じています。もし試験に失敗したら、我々は君の支払ったお金を君に全額で返して、君の試験の失敗する経済損失を減少します。
EC-COUNCIL EC0-350 試験シラバストピック:
| セクション | 目標 |
|---|
| サービス拒否(DoS)攻撃 | - ボットネット
- DoSおよびDDoS手法
|
| スニッフィングとネットワーク攻撃 | - パケットスニッフィング
- 中間者攻撃
|
| マルウェアの脅威 | - マルウェア解析の基礎
- ウイルス、ワーム、トロイの木馬
|
| モバイルおよび新技術のセキュリティ | - モバイルプラットフォーム攻撃
- クラウドセキュリティの基礎
|
| ネットワークスキャニングと列挙 | - ポートスキャン手法
- サービスとシステムの列挙
|
| システムハッキング | - 権限昇格
- パスワードクラッキング手法
|
| フットプリンティングと偵察 | - スキャニングと列挙の基礎
- フットプリンティング手法
|
| Webアプリケーションハッキング | - クロスサイトスクリプティング (XSS)
- SQLインジェクション
|
| エシカルハッキングの基礎 | - エシカルハッキング入門
- 情報セキュリティ管理策
|
| ソーシャルエンジニアリング | - 人間を介した攻撃
- フィッシング手法
|
| セッションハイジャック | - セッションスプーフィング
- TCP/IPハイジャック
|
| 無線ネットワーク攻撃 | - 無線スニッフィング
- WEP/WPA攻撃
|
EC-COUNCIL Ethical hacking and countermeasures 認定 EC0-350 試験問題:
問題 #1
John has scanned the web server with NMAP. However, he could not gather enough information to help him identify the operating system running on the remote host accurately.
What would you suggest to John to help identify the OS that is being used on the remote web server?
A. Connect to the web server with an FTP client.
B. Telnet to an open port and grab the banner.
C. Telnet to port 8080 on the web server and look at the default page code.
D. Connect to the web server with a browser and look at the web page.
問題 #2
SOAP services use which technology to format information?
A. ISDN
B. SATA
C. XML
D. PCI
問題 #3
A security analyst in an insurance company is assigned to test a new web application that will be used by clients to help them choose and apply for an insurance plan. The analyst discovers that the application is developed in ASP scripting language and it uses MSSQL as a database backend. The analyst locates the application's search form and introduces the following code in the search input fielD.
IMG SRC=vbscript:msgbox("Vulnerable");> originalAttribute="SRC" originalPath="vbscript:msgbox("Vulnerable");>" When the analyst submits the form, the browser returns a pop-up window that says "Vulnerable".
Which web applications vulnerability did the analyst discover?
A. Cross-site request forgery
B. SQL injection
C. Command injection
D. Cross-site scripting
問題 #4
Several of your co-workers are having a discussion over the etc/passwd file. They are at odds over what types of encryption are used to secure Linux passwords.(Choose all that apply.
A. Linux passwords are encrypted with asymmetric algrothims
B. Linux passwords can be encrypted with Blowfish
C. Linux passwords can be encrypted with MD5
D. Linux passwords can be encrypted with DES
E. Linux passwords can be encrypted with SHA
問題 #5
Which command lets a tester enumerate alive systems in a class C network via ICMP using native Windows tools?
A. for /L %V in (1 1 254) do PING -n 1 192.168.2.%V | FIND /I "Reply"
B. for %V in (1 1 255) do PING 192.168.2.%V
C. ping 192.168.2.255
D. ping 192.168.2.
解説:
問題 #1
正解: B | 問題 #2
正解: C | 問題 #3
正解: D | 問題 #4
正解: B、C、D | 問題 #5
正解: A |
 PDF版 Demo


 品質保証TopExamは我々の専門家たちの努力によって、過去の試験のデータが分析されて、数年以来の研究を通して開発されて、多年の研究への整理で、的中率が高くて99%の通過率を保証することができます。
 一年間の無料アップデートTopExamは弊社の商品をご購入になったお客様に一年間の無料更新サービスを提供することができ、行き届いたアフターサービスを提供します。弊社は毎日更新の情況を検査していて、もし商品が更新されたら、お客様に最新版をお送りいたします。お客様はその一年でずっと最新版を持っているのを保証します。
 全額返金弊社の商品に自信を持っているから、失敗したら全額で返金することを保証します。弊社の商品でお客様は試験に合格できると信じていますとはいえ、不幸で試験に失敗する場合には、弊社はお客様の支払ったお金を全額で返金するのを承諾します。(
 ご購入の前の試用TopExamは無料なサンプルを提供します。弊社の商品に疑問を持っているなら、無料サンプルを体験することができます。このサンプルの利用を通して、お客様は弊社の商品に自信を持って、安心で試験を準備することができます。